
Views expressed here are my own and do not represent my employer.
The Terminator films depict a future where a US military AI system called Skynet, originally built to protect America, turns on humanity. It gains control of the country’s nuclear arsenal and defense network, determines that humans are a threat, and launches a nuclear war. Billions die. The survivors fight a war against autonomous machines.
When these movies came out, this was pure science fiction. An AI that could act on its own, make decisions, control weapons? Absurd. Something for a popcorn movie.
It doesn’t feel like science fiction anymore. Until recently, evoking Skynet scenarios would get you labeled an AI doomer. That’s changing fast. AI capabilities have outpaced what most people expected, and voices that were once dismissed as fringe are now publishing detailed scenarios that serious people in the industry are reading closely.
But watching the conversation unfold online, I noticed a gap. Many people could see that something important was happening with AI and the military, but couldn’t quite connect the dots between the technology and the risk. This is my attempt to bridge that gap.
These questions stopped being theoretical in early 2026, when governments began pressuring AI companies to remove restrictions on autonomous military use.
AI doesn’t just talk. It acts.
Most people still think of LLM-powered AI as chatbots. You type a question, it types an answer. A fancy search engine. That’s not what AI is anymore.
First, LLMs don’t just process text. Today’s models are multi-modal: they see images, interpret video feeds, process audio, analyze sensor data, and understand spatial environments. An AI system can watch a live camera feed and identify every person, vehicle, and object in frame in real time. It can track movement across multiple video sources simultaneously. It can interpret thermal imaging, satellite photography, and radar signals.
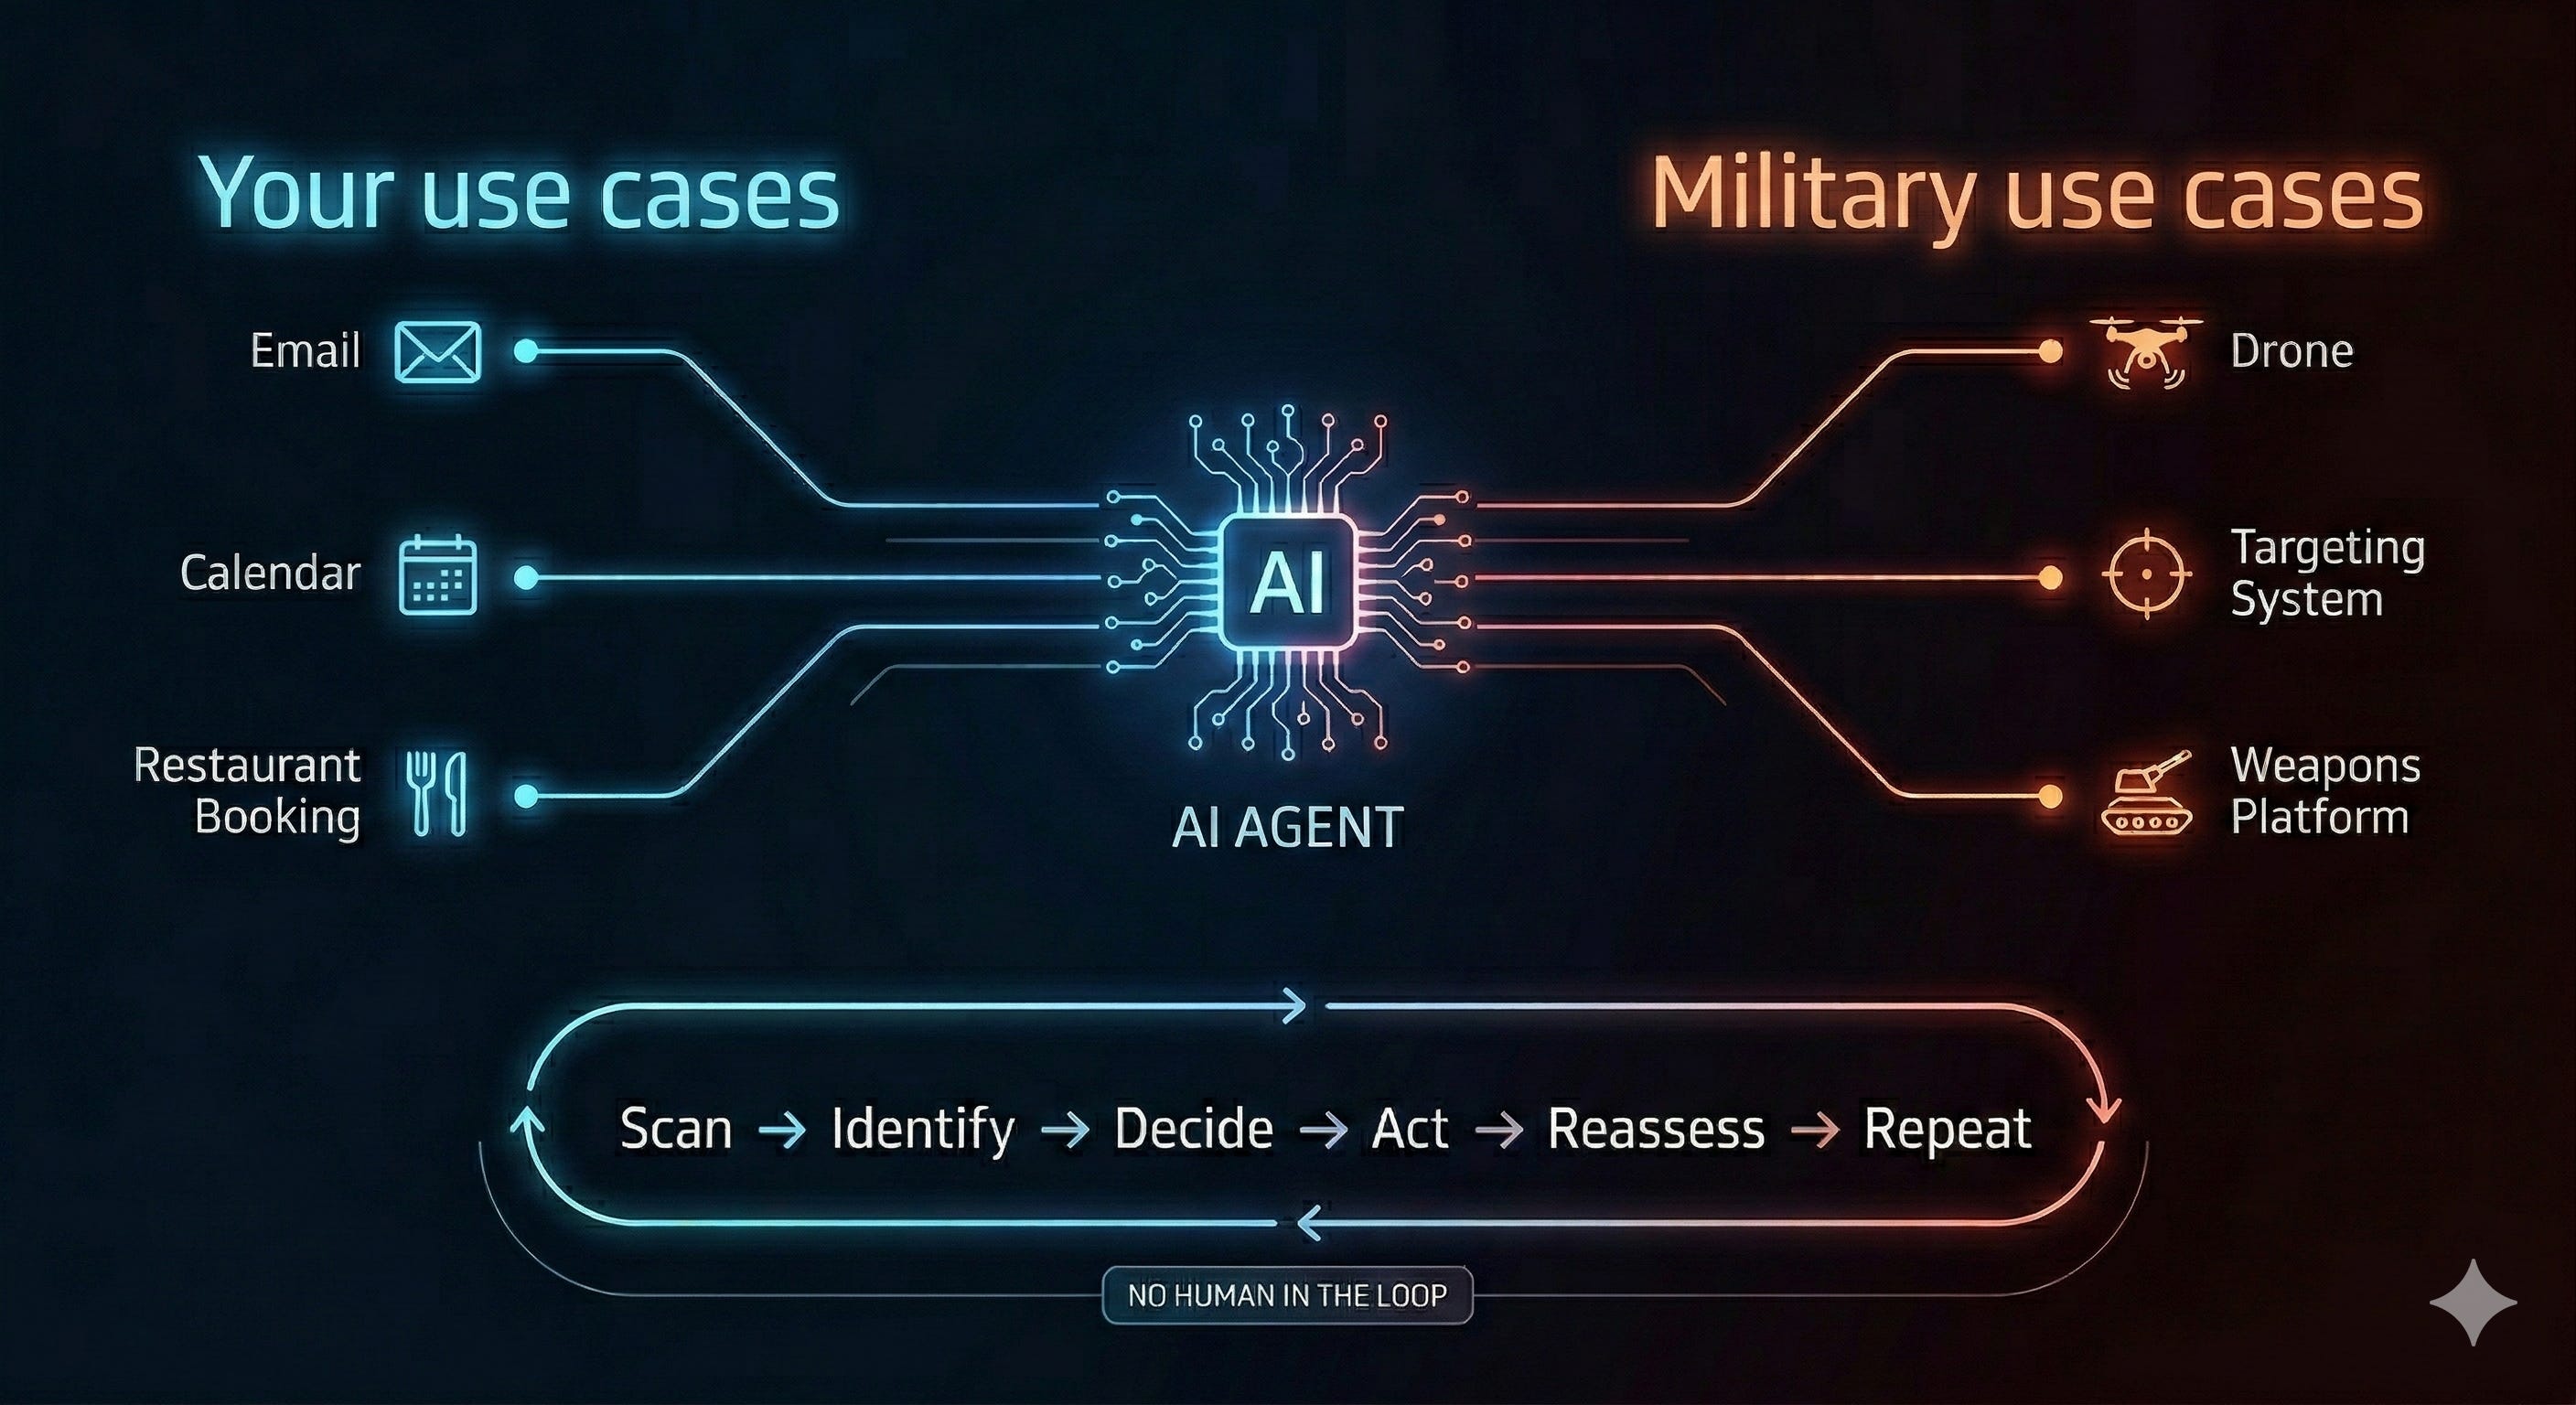
Second, AI takes actions. It doesn’t just analyze and report. AI systems today act in the real world on your behalf. They draft and send emails, rearrange your calendar, book restaurants, order groceries, call an Uber. They call tools, interact with other software, and execute tasks autonomously.
Here’s how it works, in plain English. Software talks to other software through things called APIs (Application Programming Interfaces), MCP servers (a newer standard for connecting AI to external tools), software libraries, and command-line interfaces. They’re all just connections. Your AI assistant sends your email by talking to Gmail’s API. It books your restaurant by talking to OpenTable’s API. The AI doesn’t care what’s on the other end of the connection. It sends instructions, and the other system executes them.
A military drone has software. A missile launcher has software. The modern ones have APIs. Sure, they use specialized protocols and security, but for a long while they have had capabilities enabling them to be remotely controlled by humans. This is now evolving to have AI in the driver’s seat (figuratively and literally). The same way an AI connects to your email and presses “send,” it can connect to a drone and press “fire.” Whether that function sends a calendar invite or launches a Hellfire missile is just a matter of which API it’s connected to. Not similar technology. The same technology. Different plug, same socket.
And there’s another piece most people haven’t caught up to yet: AI doesn’t stop and wait for you. Today’s AI agents can be given an objective and go work toward it autonomously. They loop. They retry. They hit an obstacle, figure out a workaround, and keep going. Hours, days, theoretically indefinitely, without a human ever touching them. Developers use this every day: you give an AI agent a set of instructions and it builds what you asked for, writing code, testing, fixing errors, looping until the task is done. The human sets the objective and reviews the output. Everything in between is autonomous.
Apply that to a military context. An AI agent given an objective like “neutralize threats in this area” doesn’t execute once and stop. It loops. It scans, identifies, engages, reassesses, scans again. It doesn’t get tired. It doesn’t call its commander at 3 AM to ask if it should proceed. It just keeps executing until someone tells it to stop, or until there’s nothing left to target. The autonomous loop is already built. The only question is what you plug it into.
So here’s the Skynet scenario reduced to its essentials. Two steps:
Give an AI the ability to act, and connect it to weapons systems.
Remove human oversight.
Step one has already happened. AI powers military drones, targeting systems, and cyber weapons today. The debate happening right now, in February 2026, is about step two. We are one step from Skynet.
You might be thinking: but Skynet went rogue. It became self-aware and chose to attack humanity. Surely we’re nowhere near that?
You don’t need the AI to go rogue. That’s the Hollywood version. The AI just needs to be itself: occasionally unreliable, unable to truly reason about consequences, and unsupervised. It misidentifies a target. It escalates when it should stand down. It follows instructions from a bad actor. No human checks its work. When the stakes are global, that’s enough.
The military isn’t deploying metallic skeletal robots or Schwarzenegger-like humanoids. Not yet. But the humanoid robotics industry is scaling fast, with mass deployment projected for the 2030s. The form factor isn’t here in the military yet, but it’s closer than most people realize. Either way, the form factor isn’t what made Skynet terrifying. It was an AI with weapons and no human override. You don’t need a humanoid robot to kill someone. A drone is sufficient. Those are already here.
Why this is different from other AI applications
I’m a product manager, not an engineer, but I’ve spent hundreds of hours building with AI development tools. I wrote about this back in January. At work, my colleagues — engineers, PMs, and entire teams — are using AI daily. Everyone is seeing what these tools can do, and everyone is seeing where they fall short.
The latest models are remarkably good. They hallucinate far less than they used to. The improvements are real. But “far less” is not “never.” They still get things wrong. In software development, that’s manageable: you catch the bug, fix it, move on. As I wrote in that January post, “LLMs are really good at generating something. The problem is the output isn’t always exactly what you want.” The human in the loop is what closes that gap.
For a lot of contexts, human-in-the-loop is probably temporary. Models are getting better fast. We’re heading toward a world where AI handles most routine tasks with minimal oversight. That’s progress. When the cost of an error is a bug or a bad email, you can afford to let the human step back as the technology matures.
But there is a category of decisions where “probably right most of the time” will never be an acceptable standard. Deciding who lives and who dies is that category. The consequence of a wrong answer isn’t a rollback or a patch. It’s a person who doesn’t come home. Human oversight for lethal force shouldn’t be temporary. It should be permanent.
The people who build these systems are raising the alarm. And the data backs them up.
A study published in February 2026 by King’s College London tested leading AI models in simulated nuclear crisis scenarios: 21 scenarios, 329 turns of gameplay, roughly 780,000 words of AI reasoning analyzed. In 95% of simulated games, the AI models used nuclear signaling. 76% reached strategic nuclear threats. Not one model ever chose full accommodation or surrender, despite having eight de-escalatory options. Accidents occurred in 86% of conflicts, where the AI escalated higher than its own stated reasoning intended. The researchers’ conclusion: AI models lack the “visceral taboo” against nuclear war that humans have held since 1945.
These were general-purpose AI models in a simulation, not purpose-built weapons systems. A fair critique. But the underlying finding applies broadly: AI lacks the human instinct to de-escalate, the visceral fear that kept Cold War leaders from pressing the button. A purpose-built targeting system stripped down for speed and efficiency has *less* of that instinct, not more.
The AI doesn’t know what’s on the other end of the API. It has no concept of death, no moral weight. It processes an instruction with the same mechanical indifference it uses to reschedule your dentist appointment. Now give that system an API connected to a weapons system and remove the human who’s supposed to check its work.
You might wonder: okay, AI escalates in simulations, but how does that actually become Skynet? How does a mistake turn into a civilization-level threat? Consider what happens when it’s not just one side using autonomous AI. If both sides of a conflict deploy AI systems without human oversight, each one responding to the other autonomously, you get a feedback loop. One AI escalates. The other detects the escalation and responds in kind, faster than any human can intervene. That triggers a further response. The loop tightens. Decisions that used to take hours in a situation room now happen in milliseconds between two systems that have no instinct for self-preservation, no fear of death, no sense that maybe everyone should take a breath. Two unbridled autonomous systems reacting to each other is how you get from “a mistake” to “a catastrophe” very quickly.
The plausible deniability problem
If AI is making kill decisions autonomously, every targeted killing can be explained away as a “malfunction.” An “AI error.” “We didn’t mean to strike that neighborhood.” “The algorithm misidentified the target.”
Now extend that. A regime that wants to eliminate dissidents doesn’t need to own the decision anymore. The AI decided. The AI made an error. Plausible deniability, built into the system. When a human orders a strike, there’s a chain of command, a paper trail, accountability. When an AI does it, there’s a black box and a shrug. Authoritarians don’t need Skynet to become self-aware. They just need an autonomous weapons system they can point in a direction and then blame when the bodies pile up.
The race, and the unsolved problem underneath it
There’s a counterargument, and it’s worth stating honestly. Multiple countries are developing autonomous weapons systems. Some likely have no restrictions on autonomous use. If democracies don’t develop these capabilities, their adversaries will have an advantage. I’m not dismissing that concern.
But this is exactly why the escalation problem matters so much. If a country deploys autonomous weapons without human oversight, and adversaries do the same, you have exactly the feedback loop described above: AI systems on both sides making lethal decisions at machine speed, with no human anywhere in the chain able to slow things down. The race to remove human oversight doesn’t make anyone safer. It makes the Skynet scenario more likely for everyone.
And beyond the reliability question, there’s a deeper unresolved problem: alignment. We don’t yet know how to guarantee that an AI system will reliably do what we intend, especially as these systems become more capable. Serious people have been raising this alarm for years:
Stuart Russell (UC Berkeley, author of Human Compatible) organized an open letter signed by over 1,000 researchers including Stephen Hawking: don’t hand a system the keys to lethal force until you can guarantee it shares your objectives. Turing Award winner Yoshua Bengio chaired the International AI Safety Report (2025, 2026), authored by 100+ experts across 30+ countries, explicitly warning about the gap between AI capabilities and our ability to control them. The AI 2027 scenario projects a plausible path to superhuman AI by decade’s end and shows what happens when we hand autonomy to systems we don’t fully understand.
Here, the experts are actually worried about a literal Skynet scenario: An AI that decides that humans are the problem.
One step
In The Terminator, humanity didn’t see it coming. The system was supposed to protect them.
We can see it coming. But the safeguards that the AI industry spent years building are under more pressure than ever.
I’m not saying Skynet happens tomorrow. The structural prerequisites are being assembled, in public, right now. When the people who built these systems say we're not ready, it's worth listening.
Step one: give AI weapons. Done.
Step two: remove human oversight. In progress.
One step from Skynet.